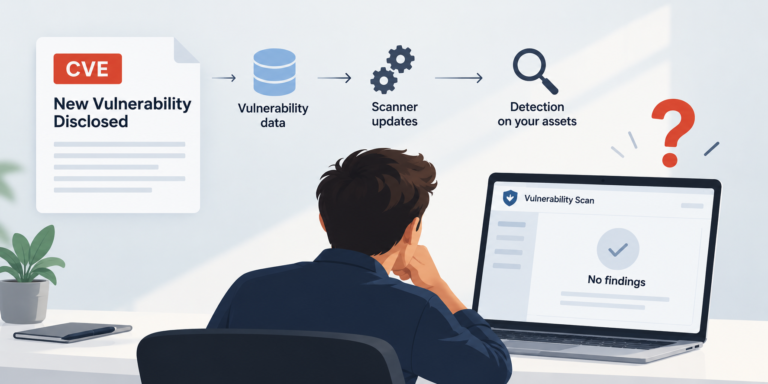
The CVE Is Public. Why Hasn’t Your Scanner Found It Yet?

What happens between a security advisory and a finding in your report—and how to act when the evidence is incomplete. A critical vulnerability makes the news. Your team checks the scanner. No findings. Someone asks the inevitable question: “Are we…
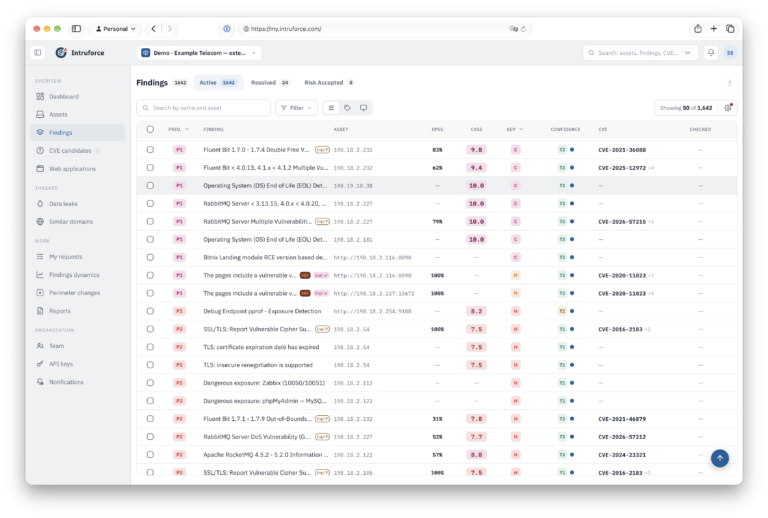
How SeguriScan Turns Scanner Alerts into Actionable Findings

A critical vulnerability appears in a report. A week later, it is gone. The team may have installed an update, restricted access to the service, or changed its configuration. But there are other possible explanations: the scanner could not reach…

AI Is Shrinking Your Window to Protect the External Perimeter

Your external attack surface is no longer something to review once a quarter. AI is making reconnaissance, vulnerability research, and exploit development faster and cheaper. That changes a basic assumption behind many security programmes: that a company has enough time…

How to Build a Vulnerability Management Process

Almost every organization today performs vulnerability scanning. However, far fewer organizations have a mature vulnerability management process. These are not the same thing. A scanner can identify thousands of vulnerabilities in a matter of hours, but it cannot decide which…

Meet CVE.Tools: The Missing Interface for CVEs

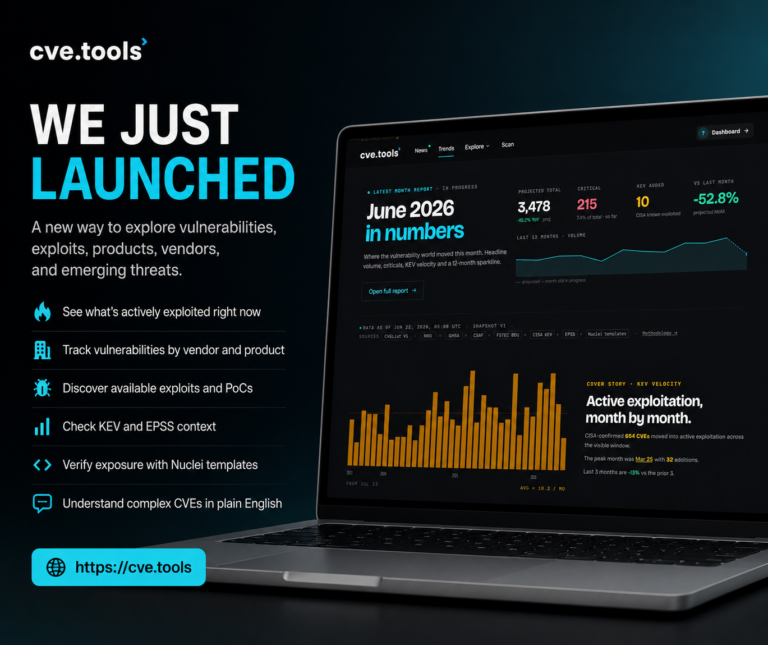
🚀 We just launched CVE.Tools A new way to explore vulnerabilities, exploits, products, vendors, and emerging threats. Instead of jumping between multiple sources, you can now:🔥 See what’s actively exploited right now🏢 Track vulnerabilities by vendor and product💣 Discover available…

Forgotten Subdomains: The Hidden Attack Surface No One Monitors

Every company has subdomains — portal.yourcompany.com, promo.yourcompany.com, dev.yourcompany.com. They appear quickly. A marketing campaign, a new test environment, a temporary landing page. Then the project ends. The budget moves on. The person who set it up leaves. And yet —…

The First 3 Security Policies Every Small Business Needs

When small businesses hear the term “security policies,” they often picture 100-page manuals, consultants, and bureaucracy.But the truth is: you only need three simple rules to start. These aren’t about red tape. They’re about protecting your data and keeping people accountable. 1.…

Shadow AI: The New Risk You Didn’t Approve

First came Shadow IT — employees adopting SaaS tools without approval.Now comes Shadow AI — employees pasting sensitive business data into chatbots and AI tools you never signed off on. It feels helpful. It feels productive.But it quietly creates a new class of risk. What…

5 Reasons to Regularly Review Your IT Outsourcing Partner

For many small and mid-sized businesses, IT outsourcing feels like peace of mind. You hand over infrastructure, updates, and user support — and assume it’s handled. But here’s the truth: outsourcing IT doesn’t mean outsourcing responsibility. Your provider may keep systems running,…