Tag CVE

The CVE Is Public. Why Hasn’t Your Scanner Found It Yet?
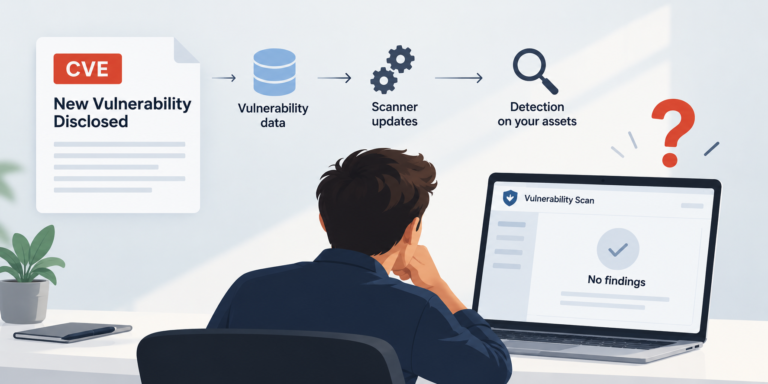
What happens between a security advisory and a finding in your report—and how to act when the evidence is incomplete. A critical vulnerability makes the news. Your team checks the scanner. No findings. Someone asks the inevitable question: “Are we…

Meet CVE.Tools: The Missing Interface for CVEs

🚀 We just launched CVE.Tools A new way to explore vulnerabilities, exploits, products, vendors, and emerging threats. Instead of jumping between multiple sources, you can now:🔥 See what’s actively exploited right now🏢 Track vulnerabilities by vendor and product💣 Discover available…