Tag Patch Management

The CVE Is Public. Why Hasn’t Your Scanner Found It Yet?
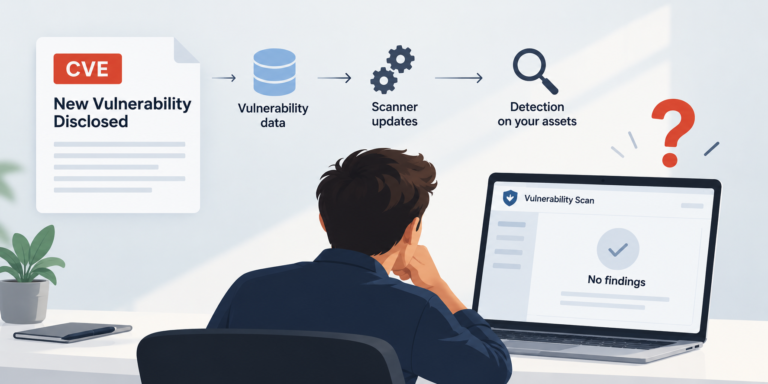
What happens between a security advisory and a finding in your report—and how to act when the evidence is incomplete. A critical vulnerability makes the news. Your team checks the scanner. No findings. Someone asks the inevitable question: “Are we…
How to Build a Vulnerability Management Process

Almost every organization today performs vulnerability scanning. However, far fewer organizations have a mature vulnerability management process. These are not the same thing. A scanner can identify thousands of vulnerabilities in a matter of hours, but it cannot decide which…