Tag vulnerability management

AI Makes Weaknesses Easier to Find. Who Will Find Yours First?
AI is making parts of an attacker’s job faster, cheaper and more accessible. Businesses need a regular way to check what they expose—and act on what they find. Your company does not need to use artificial intelligence to be affected…
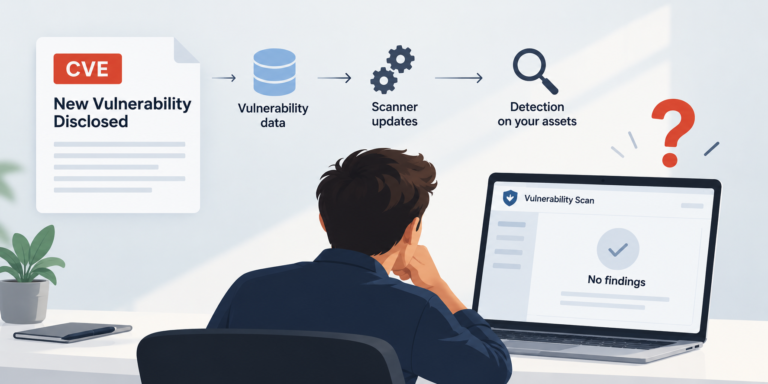
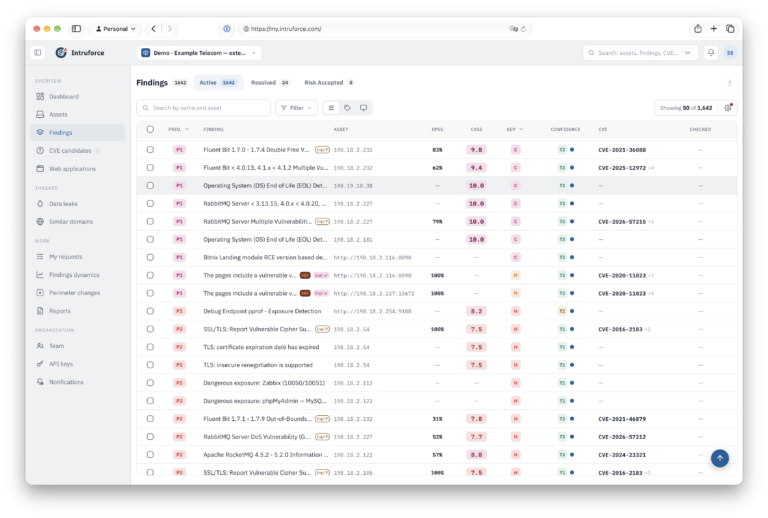
The CVE Is Public. Why Hasn’t Your Scanner Found It Yet?

What happens between a security advisory and a finding in your report—and how to act when the evidence is incomplete. A critical vulnerability makes the news. Your team checks the scanner. No findings. Someone asks the inevitable question: “Are we…

How SeguriScan Turns Scanner Alerts into Actionable Findings

A critical vulnerability appears in a report. A week later, it is gone. The team may have installed an update, restricted access to the service, or changed its configuration. But there are other possible explanations: the scanner could not reach…

AI Is Shrinking Your Window to Protect the External Perimeter

Your external attack surface is no longer something to review once a quarter. AI is making reconnaissance, vulnerability research, and exploit development faster and cheaper. That changes a basic assumption behind many security programmes: that a company has enough time…

How to Build a Vulnerability Management Process

Almost every organization today performs vulnerability scanning. However, far fewer organizations have a mature vulnerability management process. These are not the same thing. A scanner can identify thousands of vulnerabilities in a matter of hours, but it cannot decide which…

Meet CVE.Tools: The Missing Interface for CVEs

🚀 We just launched CVE.Tools A new way to explore vulnerabilities, exploits, products, vendors, and emerging threats. Instead of jumping between multiple sources, you can now:🔥 See what’s actively exploited right now🏢 Track vulnerabilities by vendor and product💣 Discover available…

Security Questions Every Founder Should Be Asking Weekly

As a founder, your calendar is packed. Investors, customers, product, hiring — security often slips to the bottom of the list. But here’s the truth: ignoring security is not saving time; it’s borrowing risk. You don’t need to be a cybersecurity…